

 USD
 USD
 GBP
 EUR
 INR
 ZAR
 AUD
 CAD
 MYR
 SGD
 THB
 HKD
 BRL
 AED
HTTP and HTTPS are protocols used to transfer data between a web browser and a web server. The key difference is security: HTTP sends data without transport encryption, while HTTPS protects the connection using TLS encryption.
That extra “S” gives HTTPS three important protections: encryption, data integrity, and server authentication. This makes HTTPS the standard choice for modern websites — not just sites that collect passwords or payment information.
HTTP vs HTTPS: Quick Comparison
| Feature | HTTP | HTTPS |
|---|---|---|
| Full form | Hypertext Transfer Protocol | Hypertext Transfer Protocol Secure |
| Data encryption | No transport encryption | Encrypted with TLS |
| Default port | 80 | 443 |
| URL scheme | http:// | https:// |
| Server authentication | Not provided by HTTP | Verified using a TLS certificate |
| Data integrity | Traffic can potentially be modified in transit | TLS makes unauthorized modification detectable |
| Browser treatment | Plaintext HTTP is treated as insecure | Protected connection when TLS is configured correctly |
| Protocol versions | Mostly limited to HTTP/1.1 for legacy and redirect use | Standard deployment for HTTP/1.1, HTTP/2, and HTTP/3 |
What Is HTTP?
HTTP is an application-layer protocol, which stands for Hypertext Transfer Protocol. It’s used to exchange resources between client and server on the web, with its shared semantics defined in the IETF’s RFC 9110: HTTP Semantics.
When you open a webpage, your browser acts as the client. It sends HTTP requests for resources like HTML, images, CSS, JavaScript, video, or API data, and the server returns HTTP responses carrying that content along with a status code, such as 200 OK for success or 404 Not Found when the resource doesn’t exist.
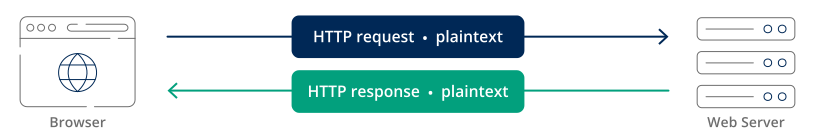
HTTP is also stateless; each request is handled on its own, and the server keeps no memory of previous requests once it responds. On its own, it doesn’t provide transport encryption, server authentication, or integrity protection. HTTP traditionally runs over port 80. If traffic crosses an untrusted network, anyone positioned to intercept the connection can potentially read or modify it.
Common HTTP Methods
HTTP methods describe what the client is asking the server to do:
- GET — retrieves a resource
- POST — submits data or creates a resource
- PUT — replaces a resource
- PATCH — partially updates a resource
- DELETE — removes a resource
- HEAD — requests headers without the response body
- OPTIONS — asks which communication options are available
These methods work the same way whether HTTP travels over an insecure connection or securely through HTTPS.
What Is HTTPS?
HTTPS is the secure version of HTTP. It stands for Hypertext Transfer Protocol Secure. HTTPS uses TLS to protect data exchanged between a web browser and a website.
You’ll still hear people call it an “SSL certificate” out of habit, but SSL was retired years ago. What’s actually doing the work on a modern HTTPS connection is TLS.
TLS protects the connection in three main ways:
- Encrypts the traffic, so anyone intercepting it sees scrambled data instead of anything readable.
- Makes tampering detectable, so if someone alters the data mid-transit, the change doesn’t slip through unnoticed.
- Authenticates the server, letting the browser confirm it’s actually talking to the site named on the certificate.
Together, these protections secure the HTTP traffic as it moves between the browser and server. HTTPS uses port 443 by default.
How Does HTTPS Work?
HTTPS works by having the browser and server complete a TLS handshake that establishes an encrypted connection, and then exchanging normal HTTP traffic through that connection.
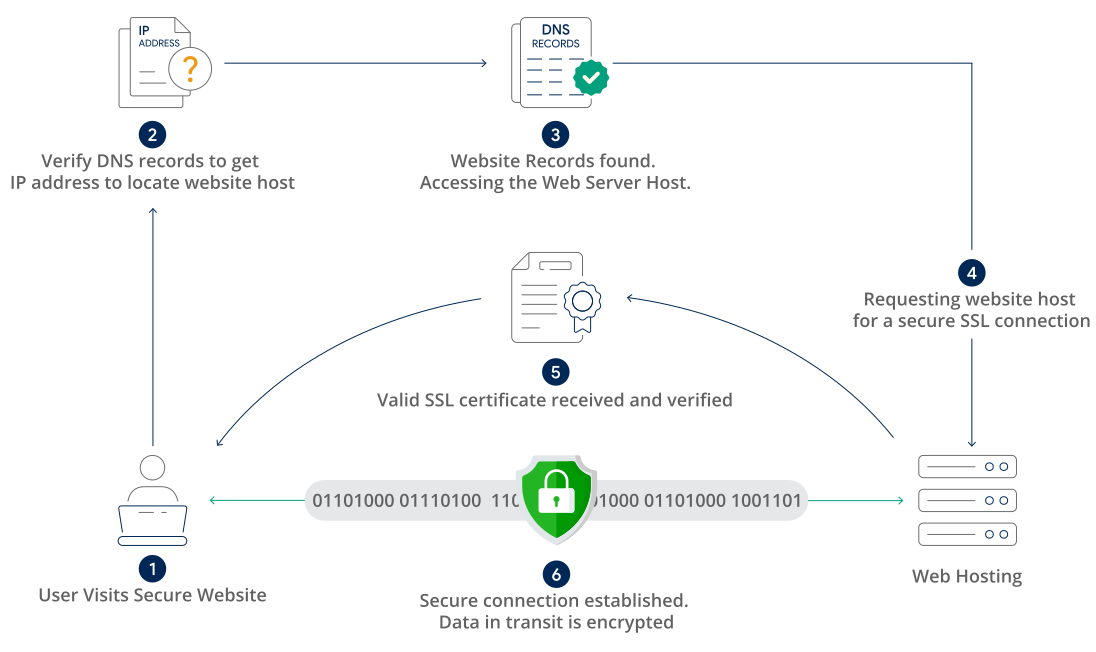
- The browser opens a TCP connection to the server on port 443 and begins a TLS handshake, agreeing on which cryptographic settings they’ll use for the connection.
- The server presents its TLS certificate, which lets the browser authenticate the server for the requested domain and supplies the public-key information the handshake needs.
- The TLS handshake establishes encryption keys. Client and server negotiate cryptographic parameters and derive shared keying material through ephemeral key exchange, generating a fresh session key for that connection rather than reusing one tied permanently to the certificate.
- HTTP traffic travels through the encrypted connection. Once the handshake finishes, normal HTTP requests and responses move back and forth securely.
The result is still HTTP at the application layer — HTTPS just means that HTTP is being carried through a connection protected by TLS.
HTTP vs HTTPS: The Security Difference
The most important difference is what happens to data while it is moving across the network.
Say a customer enters a password. Over plain HTTP, the connection does not protect that information with TLS. An attacker positioned on the network may be able to intercept or alter the traffic.
With HTTPS, TLS encrypts the connection before the password is transmitted. Someone intercepting the connection sees encrypted application data rather than readable HTTP content.
The same protection extends to cookies, search queries, form submissions, API requests, page content, and session information; along with login fields.
Does HTTPS Mean a Website Is Safe?
No. HTTPS tells you the connection between your browser and the server is encrypted and authenticated. It does not prove that the website owner is trustworthy or that the content itself is harmless. A phishing site can also obtain a valid TLS certificate and use HTTPS. Having HTTPS does not mean that the company behind the website is honest or safe to do business with.
HTTP/1.1, HTTP/2 and HTTP/3 vs HTTPS
HTTPS is HTTP protected by TLS, and it applies regardless of version – HTTP/1.1, HTTP/2, and HTTP/3 are separate generations of the protocol that determine how data is packaged and transported.
HTTP/1.1
Released in 1997, HTTP/1.1 is the long-standing, text-based version of HTTP. It handles requests one after another, so a single slow file can hold up everything queued behind it.
HTTP/2
Introduced in 2015, HTTP/2 switched to a binary format and added multiplexing, letting multiple files travel over a single connection at the same time. Header compression trims repeated data from every request, though a lost packet can still stall the whole connection.
HTTP/3
The newest version, from 2022, HTTP/3 replaces TCP with QUIC and builds TLS 1.3 directly into how the connection is established rather than layering it on afterward. Because QUIC handles streams independently, packet loss affecting one stream does not have to hold up the others in the same way TCP-level loss can affect HTTP/2. This can improve performance on high-latency or unstable networks.
That is why “HTTP is faster because it skips encryption” is not a useful modern comparison. Real-world performance depends on protocol version, latency, connection reuse, server configuration, caching, and CDN use – not simply on whether TLS is present.
Why Should Websites Use HTTPS?
Websites should use HTTPS because it protects data in transit, helps prevent network-level tampering, authenticates the server, and supports security features built into modern browsers.
-
Protect data in transit
HTTPS keeps web traffic from traveling as readable plaintext. That matters even for informational sites, since cookies, sessions, URLs, forms, and API calls can all carry data worth protecting, not just login pages.
-
Prevent traffic tampering
TLS integrity protection makes it much harder for someone between the browser and server to silently alter what’s being sent. Without it, an attacker on the same network could inject malicious ads or malware into an otherwise legitimate page before it ever reaches the visitor.
-
Authenticate the server
A trusted TLS certificate lets the browser verify that the server presenting it is actually valid for the requested domain, rather than something impersonating it.
-
Support the modern web platform
Browsers treat HTTPS pages as secure contexts, and several powerful features, including geolocation, service workers, camera and microphone access, and Web Authentication, are restricted to those contexts.
-
Support search visibility
Google has used HTTPS as a lightweight ranking signal since 2014. It doesn’t replace content quality, relevance, links, or technical SEO, but it remains part of a sound technical foundation.
How Can You Tell Whether a Site Uses HTTP or HTTPS?
The address bar gives it away immediately once you look at the URL prefix.
Click or double-click directly inside the address bar. It will show:
- https:// means the connection is encrypted
- http:// means it isn’t
Next to the address, every browser also has a site-information icon (tune, padlock, or shield). Clicking it shows:
- Certificate details – who issued it and when it expires
- Mixed content warning – the site is HTTPS, but some images or scripts are still loading unencrypted
- “Not Secure” label or warning triangle – the site is plain HTTP. Don’t enter passwords, card numbers, or other private information.
How to Move a Website From HTTP to HTTPS
Moving a website from HTTP to HTTPS takes more than installing a certificate. Here’s the full process:
- Back up your website files and database before making any changes, so you have a clean rollback point if something goes wrong partway through.
- Obtain a trusted TLS certificate covering the required domain names.
- Install and configure it on the web server, CDN, load balancer, or hosting platform.
- Make every page and resource available through HTTPS.
- Update internal links, scripts, stylesheets, images, canonical URLs, hreflang references, and XML sitemaps.
- Redirect each HTTP URL to its equivalent HTTPS URL using a permanent redirect.
- Check for mixed content caused by resources still loading over HTTP.
- Update Search Console, analytics, ad platforms, CDNs, APIs, webhooks, and other integrations where needed. (Since Google treats HTTP and HTTPS as separate properties in Search Console, this means adding the HTTPS version as its own property rather than assuming the existing one carries over).
- Test the certificate chain, supported TLS versions, redirects, and key user journeys.
- Consider enabling HTTP Strict Transport Security (HSTS) once HTTPS is confirmed to be working correctly.
HTTP vs HTTPS FAQs
Does HTTPS hide the domain name I’m visiting?
Can a phishing site use HTTPS?
Do I still need HSTS if my site already has HTTPS?
How do I move a WordPress site from HTTP to HTTPS?
HTTP or HTTPS: Which Should You Use?
For a modern public website, the answer is HTTPS.
HTTP remains a foundational web protocol, but sending traffic without TLS leaves the connection open to interception and modification, while HTTPS adds the encryption, integrity protection, and server authentication expected as the baseline for the modern web.
Moving from HTTP to HTTPS takes more than installing a certificate. Redirects, internal URLs, mixed content, TLS configuration, and ongoing certificate renewal all need to be handled correctly. If you’re planning a migration, start by identifying which domains and subdomains need coverage, then choose a certificate that matches that scope, whether that’s a single-domain, wildcard, or multi-domain certificate.
A valid TLS certificate is what turns HTTP into HTTPS, encrypting your traffic, verifying your server’s identity, and keeping your visitors’ data safe. Get yours from CheapSSLShop and secure your site in minutes.


